Why Chat History Is a Long-Term Security Liability
Every message you keep is an asset today and a liability later. Why retention is a security decision, and how to work out what your archive is actually holding.
By Inkrypt Editorial
Read articleSecurity insights
Long-form writing on how encryption actually works, what the common claims mean, and how to move sensitive information around without leaving copies behind. Written by the people who build the product being described.
Security writing on the open web has a quality problem. A great deal of it is produced at volume by writers who have read specifications but never shipped the thing being described, and it shows: the advice is defensible in principle and useless in practice.
Everything here is written or technically reviewed by someone who has worked on the relevant code, checked against primary sources, and dated so you can judge whether it has gone stale. The process is documented on our editorial policy page.
Every message you keep is an asset today and a liability later. Why retention is a security decision, and how to work out what your archive is actually holding.
By Inkrypt Editorial
Read articleA pasted credential does not sit in one place. It sits in four, each with its own retention rule — and deleting your copy reaches exactly one of them.
By Inkrypt Editorial
Read articleKey length decides whether an attacker can read your data. The cipher mode decides whether they can change it unnoticed — and only one of those fails silently.
By Inkrypt Security Team
Read articleA salt is not a secret and does not make one password harder to guess. What it does is destroy the economics of cracking many at once. A worked example.
By Inkrypt Security Team
Read articleWhy memory-hardness is the real difference between PBKDF2 and Argon2, what each costs an attacker, and when the older function is still the right answer.
By Inkrypt Security Team
Read articleWhat window.crypto.subtle actually does, the four calls between a password and stored ciphertext, and the mistakes that survive code review.
By Inkrypt Security Team
Read article
Three categories that get confused for each other. What each is built to do, which fits the information you have, and when none of them is right.
By Inkrypt Editorial
Read article
How to evaluate an encrypted note tool: the recovery question, a one-minute browser test, where the key travels, and what deletion actually means.
By Inkrypt Security Team
Read article
The safest ways to share passwords online, why plain text credentials in email or chat are risky, and how secure sharing tools help protect your data.
By Inkrypt Editorial
Read article
Learn the difference between self-destructing notes and encrypted email, when to use each for sensitive information, and how to protect confidential data.
By Inkrypt Editorial
Read article
AES vs RSA encryption explained, then the decision itself: why Inkrypt encrypts note content with AES-256-GCM, and why RSA was the wrong tool for it.
By Inkrypt Security Team
Read article
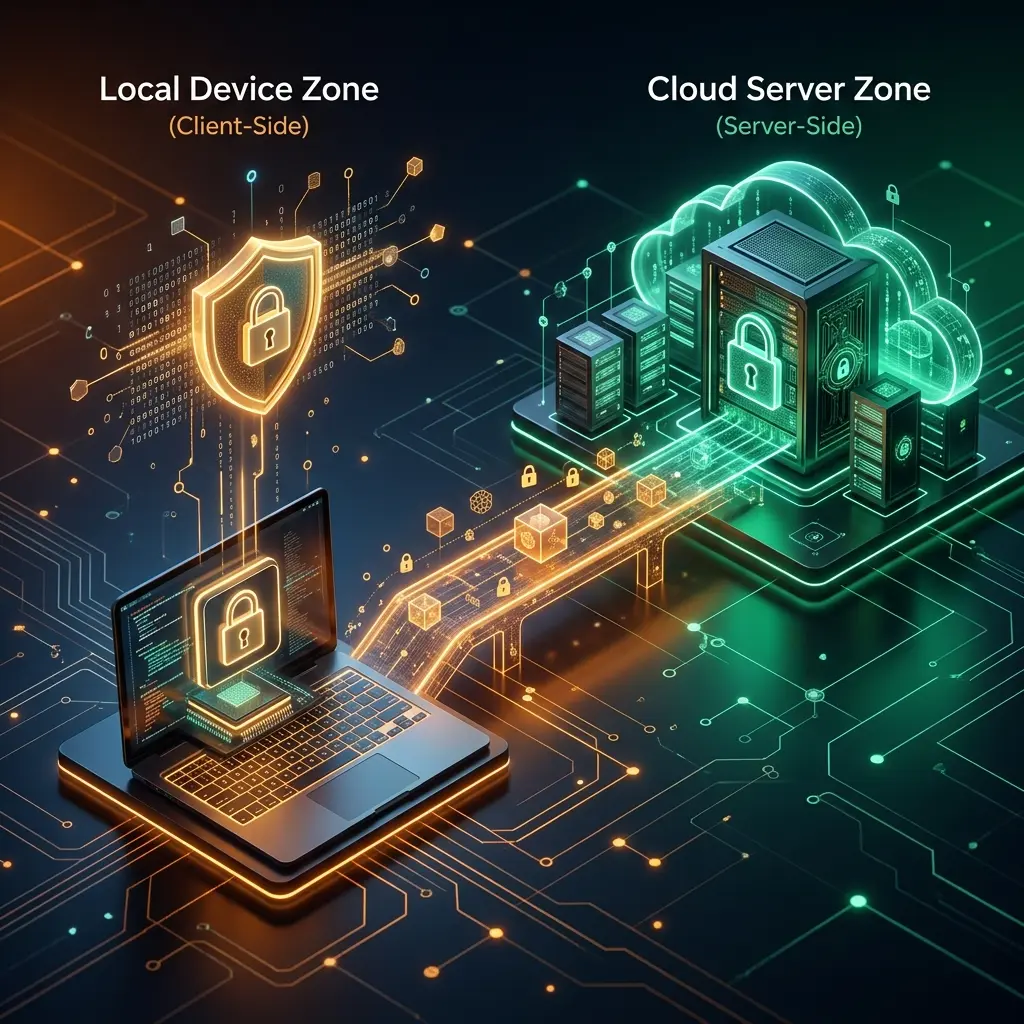
Learn the difference between client-side encryption and server-side encryption, how they protect your data, and which option is best for your privacy needs.
By Inkrypt Security Team
Read article
How browser notepads that need no account work: where notes are stored, what happens when the tab closes, and how five real tools compare.
By Inkrypt Editorial
Read article
Zero-knowledge encryption explained: what it means, how it works, how it differs from standard cloud encryption, and how to verify a service really uses it.
By Inkrypt Security Team
Read articleIf you are new to this material, the articles build on each other in roughly this order — and the reference pages below them are the fastest route to a concrete answer.
The most abused phrase in privacy marketing, and how to test any claim in four questions.
Read moreWhere the encryption runs determines who has to be trusted. The single most useful distinction here.
Read moreThe same concepts applied to a real system, with exact algorithms and parameters.
Read moreForty terms defined plainly, each with the practical consequence of getting it wrong.
Read more